 by MustafaMukhtar, MBA, ITIL
Consultant/Content Contributor, E-N Computers
20+ years of experience in IT management, project planning, enterprise systems and user support
Updated July 22, 2026
A defense contractor recently called our office asking about CMMC consulting. The conversation went well until he asked how long compliance would take.
“Typically, 12 to 18 months,” our team explained.
“Oh. Well, another company quoted me 45 days, so I’m just going to go with them.”
He hung up before we could explain why that timeline is—let’s be diplomatic—optimistic.
Here’s the reality: you could technically become CMMC compliant in 45 days. You’d just have to accept all CUI by fax machine in a locked room and never actually do anything with it.
Congratulations. You’re compliant. You’re also out of business.
For years, the Cybersecurity Maturity Model Certification (CMMC) felt like a distant “someday” requirement. That changed when November 2025 when Level 1 and Level 2 self-assessment requirements took effect, and it changed again in July 2026, when the Department of War paused Phase 2. Phase 2 would have required Level 2 contractors to pass a third-party assessment before award.
The third-party assessment is what’s paused. For now, most contractors are working toward a defensible self-assessment instead—figure on that taking about a year. Paused isn’t canceled, though, so the prep you do now still counts when it returns. The timelines below assume Phase 2 come back in some form once a 60-day review of the program wraps up in September 2026.
The market is full of “compliance in a box” solutions and vendors promising easy, done-for-you certification. Some of these tools are fully compliant—until you actually try to do something productive, like edit a document or collaborate with your team. Others rely on auditors who don’t ask hard questions.
That approach might get you a certificate. It won’t get you a security posture that survives contract performance or a DoW audit.
The real question is no longer whether you need CMMC, but how long it will take to get there—and get there in a way that doesn’t cripple your operations. The answer depends on where your security stands today, how CUI flows through your organization, and whether you’re starting from scratch or building on existing controls.
Here’s a step-by-step guide on what’s involved in CMMC compliance, how long each step is likely to take, and what you can do to make it move as quickly as possible – while still being able to run your business.
QUICK ANSWER:
How long does CMMC compliance take?
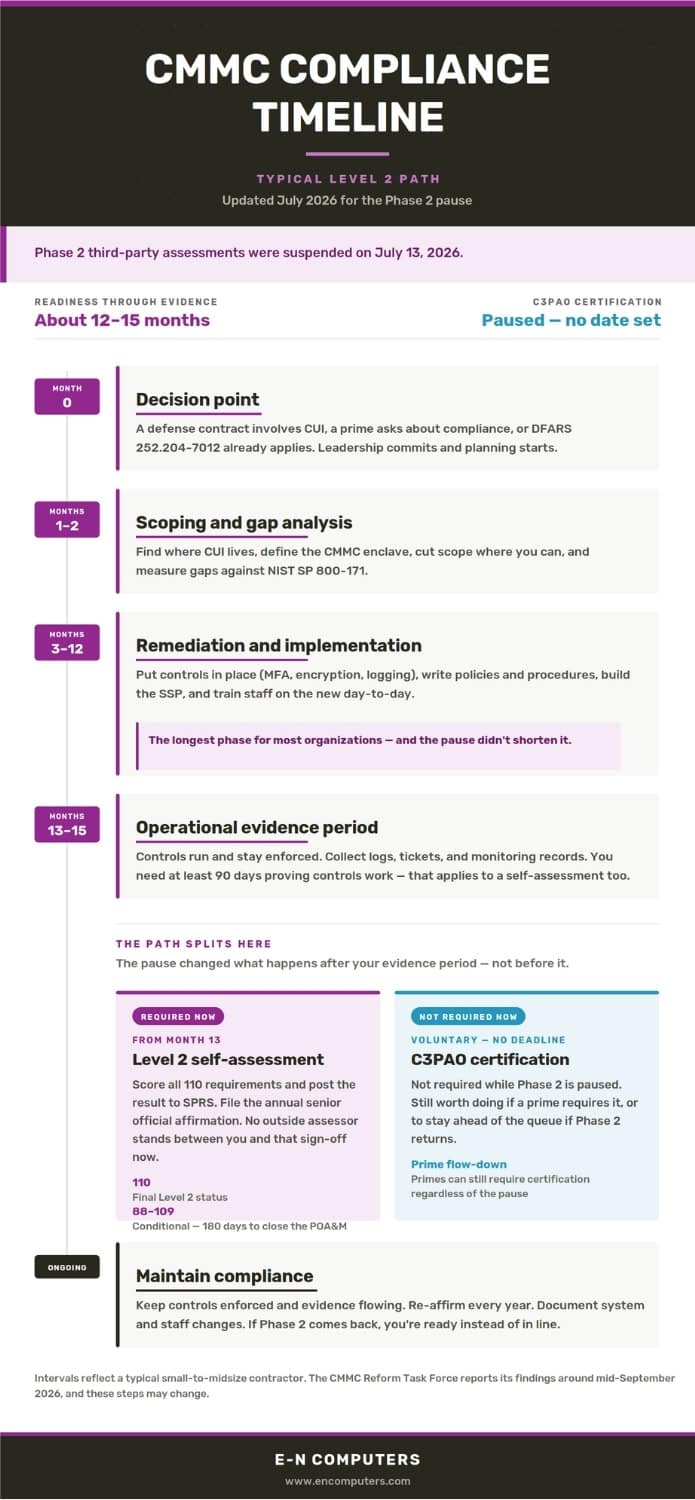
For most small-to-mid-sized defense contractors, CMMC compliance still takes 12–18 months from initial scoping to full readiness — the work hasn’t changed, even though the enforcement timeline has.
- CMMC Level 1: 1–3 months (self-assessment)
- CMMC Level 2: 12–18 months to build the program; third-party assessment is paused as of July 2026 pending a 60-day DoW review, but self-assessment is still required
- CMMC Level 3: 18+ months (government-led assessment)
“You could become compliant by just saying, ‘I’m only going to accept CUI by fax machine in a locked room,’ and then you’re compliant,” Ian MacRae, president of E-N Computers and CMMC Registered Practitioner
Why can’t most companies reach CMMC compliance faster?
Technically, timelines that are faster than 12 to 18 months are possible.
Organizations with a dedicated budget, small user counts, and a full migration into a pre-configured compliant environment—such as a GCC High enclave—can reach readiness in as little as six months.
For most organizations, however, budget is the constraint. Hardware upgrades, licensing changes, consulting support, and staff time are often spread across a fiscal year, extending the overall timeline.
The real cost of CMMC Level 2 compliance
Level 2 compliance is not a small upgrade. Thus budget constraints are the most common reason CMMC timelines stretch beyond 12 months. CMMC often requires organizations to double their existing IT and security budget.
Typical cost ranges for CMMC Level 2:
- Small organizations (10–25 users): $75,000–$150,000
- Mid-sized organizations (25–100 users): $150,000–$300,000
- Larger or complex environments: $300,000+
These costs reflect three primary drivers: consulting, tools, and time.
Most organizations require a lot more hands-on consulting during CMMC preparation. Instead of quarterly check-ins, compliance efforts often demand monthly or even weekly working sessions to stay on track. At typical consulting rates, this alone can add thousands per month.
The largest hidden cost is internal time. Managing compliance internally means learning complex tools, mapping them to NIST SP 800-171 controls, maintaining documentation, and collecting evidence. Organizations that lack dedicated security staff often underestimate this effort.
Finally, organizations should budget for the C3PAO assessment itself. With Phase 2 paused, that third-party assessment isn’t required right now—during the review, Level 2 is met through self-assessment, but the requirement is suspended, not canceled, so it’s worth planning for. Third-party assessments are typically conducted by multiple certified assessors over several days, with costs commonly ranging from $30,000 to $50,000 per location, increasing for multi-site environments.
Organizations that spread these costs across a fiscal year often extend their compliance timeline to 18 months by necessity, not choice. With the November 2026 deadline gone for now, that longer timeline is less of a forced march. The pause gives you room to phase the work on your own schedule instead of racing an assessment date — but the work, and its cost, is the same whenever the requirement comes back.
Who should start now (and who can wait)
Start now
CMMC requirements are appearing directly in the Requirements sections of DoW solicitations. If you wait until an RFP is released to begin 12 months of compliance work, the opportunity is already gone. Compliance must be in place before the bid — whether the requirement in front of you is a self-assessment or, eventually, a restored third-party certification.
One exception: the DoW clarified on July 14, 2026 that any active solicitation already carrying a Level 2 C3PAO or Level 3 requirement must be amended to strip it out, and existing contracts will have it removed at the next option period or administrative modification. If you’re bidding on something like that right now, ask the contracting officer where that amendment stands — it isn’t automatic.
Who can wait (for now)
A small group of organizations may be able to delay full CMMC preparation:
- Companies that do not handle CUI and only support DoW work indirectly
- Vendors providing commercial off-the-shelf (COTS) products with no access to controlled data
- Organizations whose DoW exposure is theoretical or long-term, with no near-term bidding plans
Even in these cases, basic scoping is still recommended. Waiting only makes sense if CUI is clearly out of scope. Typical CMMC deadlines are:
- CMMC Level 1: 1–3 months (self-assessment)
- CMMC Level 2: 12–18 months (third-party certification)
- CMMC Level 3: 18+ months (government-led assessment)
CMMC Level 3 applies to a small group of contractors supporting high-priority or mission-critical DoW programs and facing advanced cyber threats. Assessments are conducted directly by the U.S. government.
Most organizations will never need Level 3. If it applied to you, the DoW would already be communicating with that requirement clearly. For the vast majority of readers, Level 2 is the highest level to plan for.
The three phases of CMMC Level 2 compliance
1. Scoping and gap analysis (months 1–2)
The most common mistake organizations make is focusing on technology too soon. Start with data, not tools.
You must identify where Controlled Unclassified Information (CUI) exists and how it moves through your organization. That includes servers, cloud systems, email, endpoints, backups, and even physical locations like printers or shared workspaces.
The goal: Define your CMMC “enclave,” the clearly defined boundary of systems, networks, and users that handle CUI and must meet compliance requirements.
The reality: Most organizations discover their CUI is far more scattered than expected. Cleaning up data flows, consolidating systems, and reducing scope often takes weeks before remediation can even begin.
How CUI scope impacts cost and timeline
CUI scope is one of the biggest drivers of both timeline and cost. When CUI is spread across multiple systems, departments, or user accounts, every one of those systems must meet all applicable controls. When CUI is contained within a clearly defined enclave, remediation becomes faster, simpler, and easier to defend during an assessment. Reducing scope early can shave months off the process.
2. The remediation marathon (months 3–12)
This is where the real work happens. For CMMC Level 2, organizations must meet all 110 controls in NIST SP 800-171. Think of it as an operational shift, not a software purchase. Here’s some of what needs to happen:
Technical remediation
- Implementing FIPS-validated encryption
- Enforcing Multi-Factor Authentication (MFA)
- Centralizing logging and monitoring
- Secure configuration and access control
Documentation and policy development
You must create and maintain a System Security Plan (SSP) that explains, in detail, how each control is met. This document becomes the foundation of your assessment—and of self-assessment you’re responsible for right now.
The culture shift
Employees must adapt to tighter access controls, new file-sharing rules, and more structured workflows. This adjustment period is often the biggest bottleneck, not the technology itself.
What slows companies down
Most delays are not caused by security tools. Common time killers include:
- CUI living in shared drives, inboxes, or personal cloud storage
- Policies that exist but are not followed consistently
- Limited IT staff unable to collect and maintain evidence
- Leadership underestimating how much daily behavior must change
CMMC readiness vs. CMMC certification
Many organizations believe they are “compliant” because controls are implemented. Readiness and certification aren’t the same thing. Readiness means controls exist and policies are written. Certification means controls are operating, monitored, and provable over time. Assessors are not there to see what could work. They are there to see what has been working.
Right now, though, most contractors aren’t heading toward a third-party certification at all. With Phase 2 paused, a defensible self-assessment is the bar — and that’s not a lighter version of the same job. The controls still have to be operating and provable. The difference is that you’re the one signing off on them, and when no outside assessor stands between you and that sign-off, the responsibility for getting it right is yours.
3. Evidence period and assessment (the third-party assessment is currently on hold)
CMMC assessments are evidence-based. You cannot “turn it on” the week before the audit.
The 90-day expectation:
Most C3PAOs expect at least three months of logs, access records, tickets, and monitoring data that show controls are consistently enforced.
Assessment scheduling:
This is the step the DoW paused in July 2026. Under the original rollout, scheduling a C3PAO could take 2–3 months because of high demand, and the assessment itself typically ran one to two weeks — an open-book review of your security setup, your documentation, and how you operate day to day. Right now that requirement is on hold pending a 60-day review. Build your evidence anyway. When Phase 2 comes back, in this form or a revised one, the contractors who kept collecting logs and records won’t be starting over.
What a C3PAO will ask for
When third-party assessments resume, they’ll follow the same structured, predictable format. Expect requests for:
- Your System Security Plan (SSP)
- Policies and procedures mapped to controls
- Evidence of enforcement (logs, alerts, tickets)
- Proof controls were active prior to the assessment
What happens if you don’t pass your CMMC assessment?
This one is on hold with the rest of Phase 2, but the mechanics are worth knowing for when assessments return.
If an assessment identifies gaps, you’ll receive a detailed findings report outlining the deficiencies.
In limited cases, minor gaps may be documented in a Plan of Action and Milestones (POA&M), allowing remediation to continue—but certification is not granted until required controls are fully met, in accordance with DoW rules and contract requirements.
Significant control failures typically require remediation followed by a reassessment, which can add three to six months to the timeline and may require additional assessment fees.
This is why the evidence period matters. Assessors expect proof that controls were operating consistently before the assessment—not enabled temporarily for audit purposes.
Next steps
CMMC is not a one-time certification you earn and forget. After passing your assessment:
- Controls must remain enforced
- Evidence must continue to be collected
- System changes and staff turnover must be documented
- Annual audits or reassessments may be required depending on your contracts
- CMMC becomes part of daily operations, not a project with an end date
Most CMMC consultants hand you a gap assessment and a remediation checklist, then leave you to figure out the rest. We don’t work that way. E-N Computers is a managed IT provider and a CMMC consultant — which means we can scope your environment, implement the technical controls, build your documentation, and keep you compliant through your three-year certification cycle. No handoff to a separate IT team. No starting over with a new vendor when it’s time to act on the recommendations.
We work best with defense contractors under 200 employees — manufacturers, engineers, and design firms where compliance intersects with operational complexity. If you’re too small for an enterprise consultant like Summit7 but too regulated to wing it, that’s exactly the gap we fill.
We’ve been working with government contractors in Virginia and the DC metro area for nearly 30 years, and our clients work directly with owner Ian MacRae and a local team — not a rotating cast of account managers. If you want to see what this looks like in practice, we’ve walked a Virginia contractor through the full process from scoping to near-certification without breaking their budget.
Complimentary review with an experienced engineer
Are you ready for CMMC?
Get a free strategic consultation to start or streamline your journey toward CMMC compliance.
Learn more about CMMC
Guides, case studies, and tools for defense contractors navigating compliance